WordPress malware removal
Google warning, strange redirects, or spam pages you never published? We confirm what is infected and what is safe to touch.
Google warning, strange redirects, or spam pages you never published? We confirm what is infected and what is safe to touch.

We snapshot first, remove injected code and rogue admins, patch the entry point, and rotate the keys.

We recheck the site, file the Google and blacklist reviews, and give you a written after-action report.
Our promise
If the site is reinfected through the same entry point within 30 days of cleanup, we clean it again at no charge. A brand-new vulnerability in an unpatched plugin is a different incident, and we will say so plainly rather than quietly billing it as the same one.
What you get
Concrete deliverables — no vague SaaS jargon. Each engagement is sized to your business and reviewed monthly.
Isolate the site where it helps, preserve logs when useful, and stop the bleeding before cosmetic fixes.
Scan uploads, themes, and mu-plugins; audit the database for injected scripts, rogue admins, and scheduled junk.
Rebuild from a verified backup when that is faster than hand-cleaning thousands of infected files.
Once the site is verifiably clean we file the Google Search Console security review, submit reconsideration requests to blacklists flagging you, recheck Safe Browsing and your sitemap, then monitor until the warnings drop.
Admin passwords, salts, API keys, FTP/SFTP, and hosting panel access reviewed and rotated with a simple handoff list.
A written summary of what happened, how they got in, what was removed, and what to watch next — no fear-mongering, just facts.
From experience
The first message is rarely “we have malware.” It is a search warning, a strange redirect, or a page that changed on its own.
Google or another engine flags the site, or search results show URLs you never published.
Published articles or pages rewritten without an editor login you recognize.
Typing the domain works; the result in Google still bounces. Direct access and the indexed URL are different tests.
Files removed during a deploy come back because the entry point was never closed.
The application or PHP version is too old for the scanner you wanted to use. That is a finding, not a reason to skip the cleanup.
Patching is part of the job. It is not a guarantee the site will stay clean.
Patterns drawn from our team’s years of agency support work.
From the support desk
Anonymized cases from our team’s years of agency support work: what the owner saw, what was actually wrong, and what we check first because of it.
Takeaway: Deleting bad files is not the same as closing the door. Until the way in is found and every password is rotated, treat a cleanup as temporary.
Takeaway: A site too old to scan is a finding in itself. Plan the update or rebuild as soon as the cleanup is done.
Takeaway: Many hacks only redirect visitors who arrive from search engines. Always test the Google result, not just the typed address.
Takeaway: Keep revision history and off-site backups. They are how you get the original words back.
Client names and identifying details removed. Outcomes are described as they happened, including the ones that needed follow-up.
After a cleanup
A cleanup that skips these steps is how reinfection starts. Use this after the site is verifiably clean.
Print this page to keep a paper copy beside the work.
We cannot promise Google will clear a warning on a timetable. We can promise the request is filed after the site is actually clean.
Client work
Named clients and live websites you can visit.
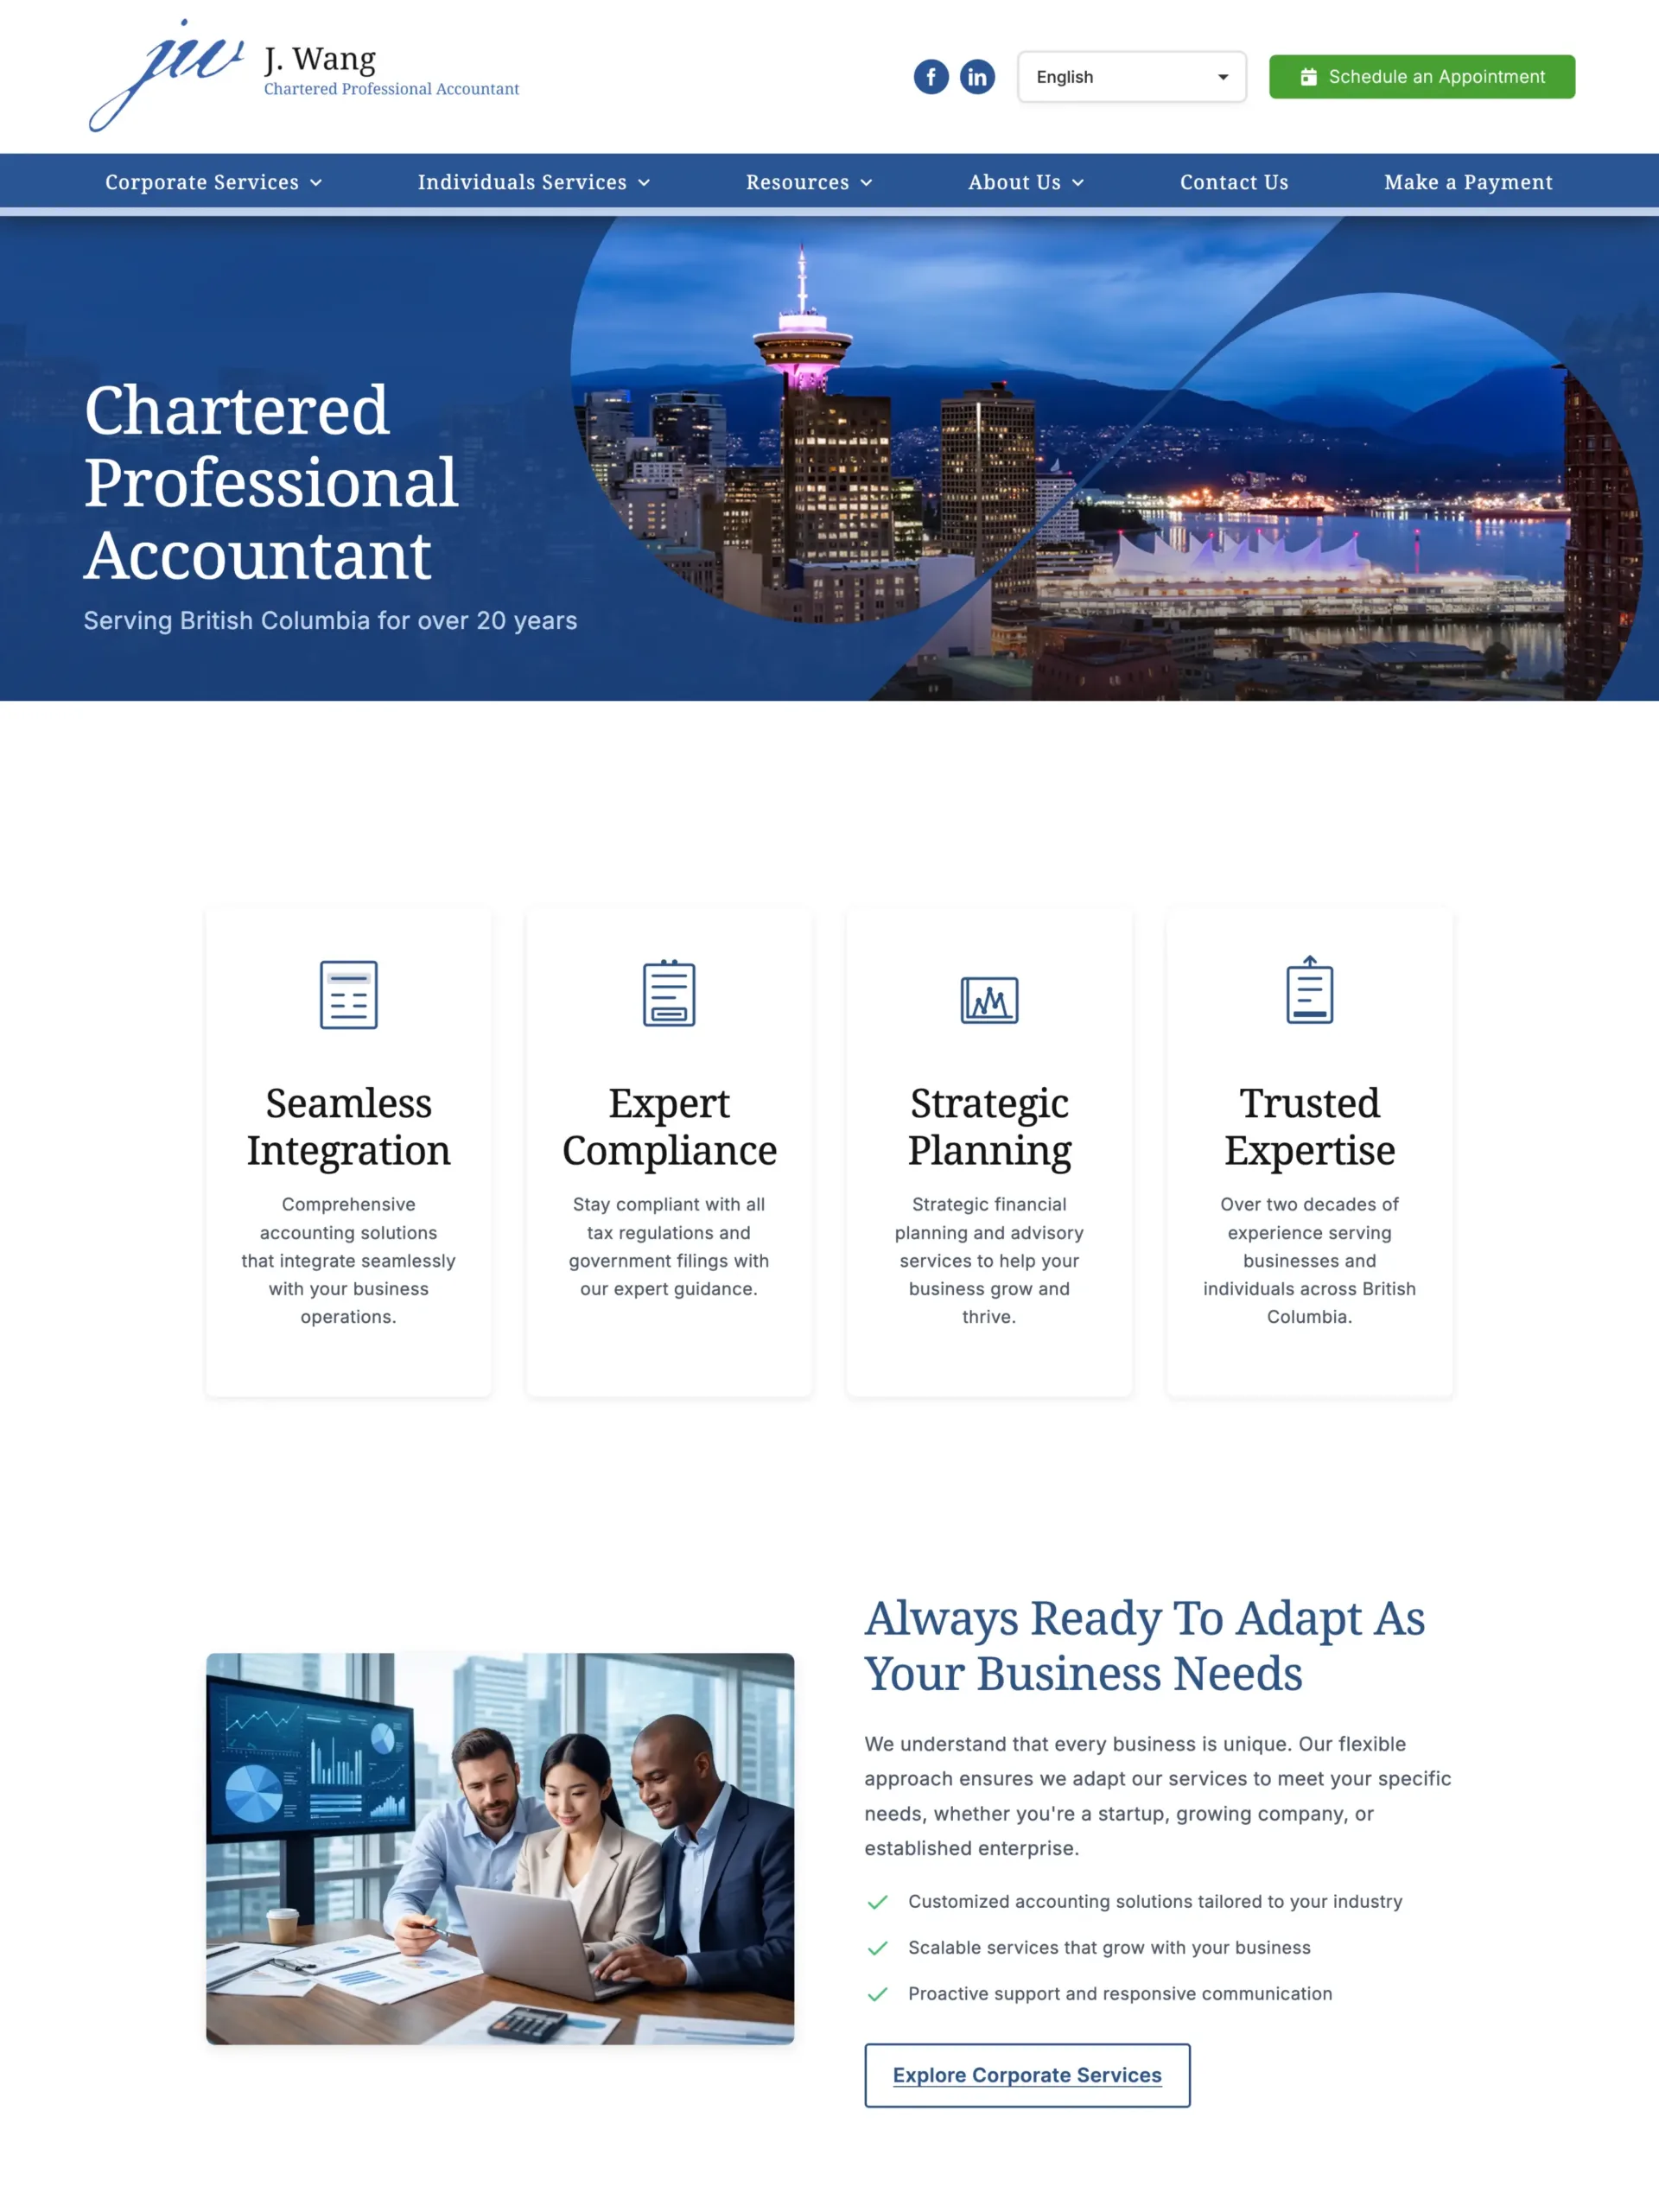
Accounting firm · Vancouver
A new professional website paired with IT support and server infrastructure (Active Directory) for a growing accounting practice.
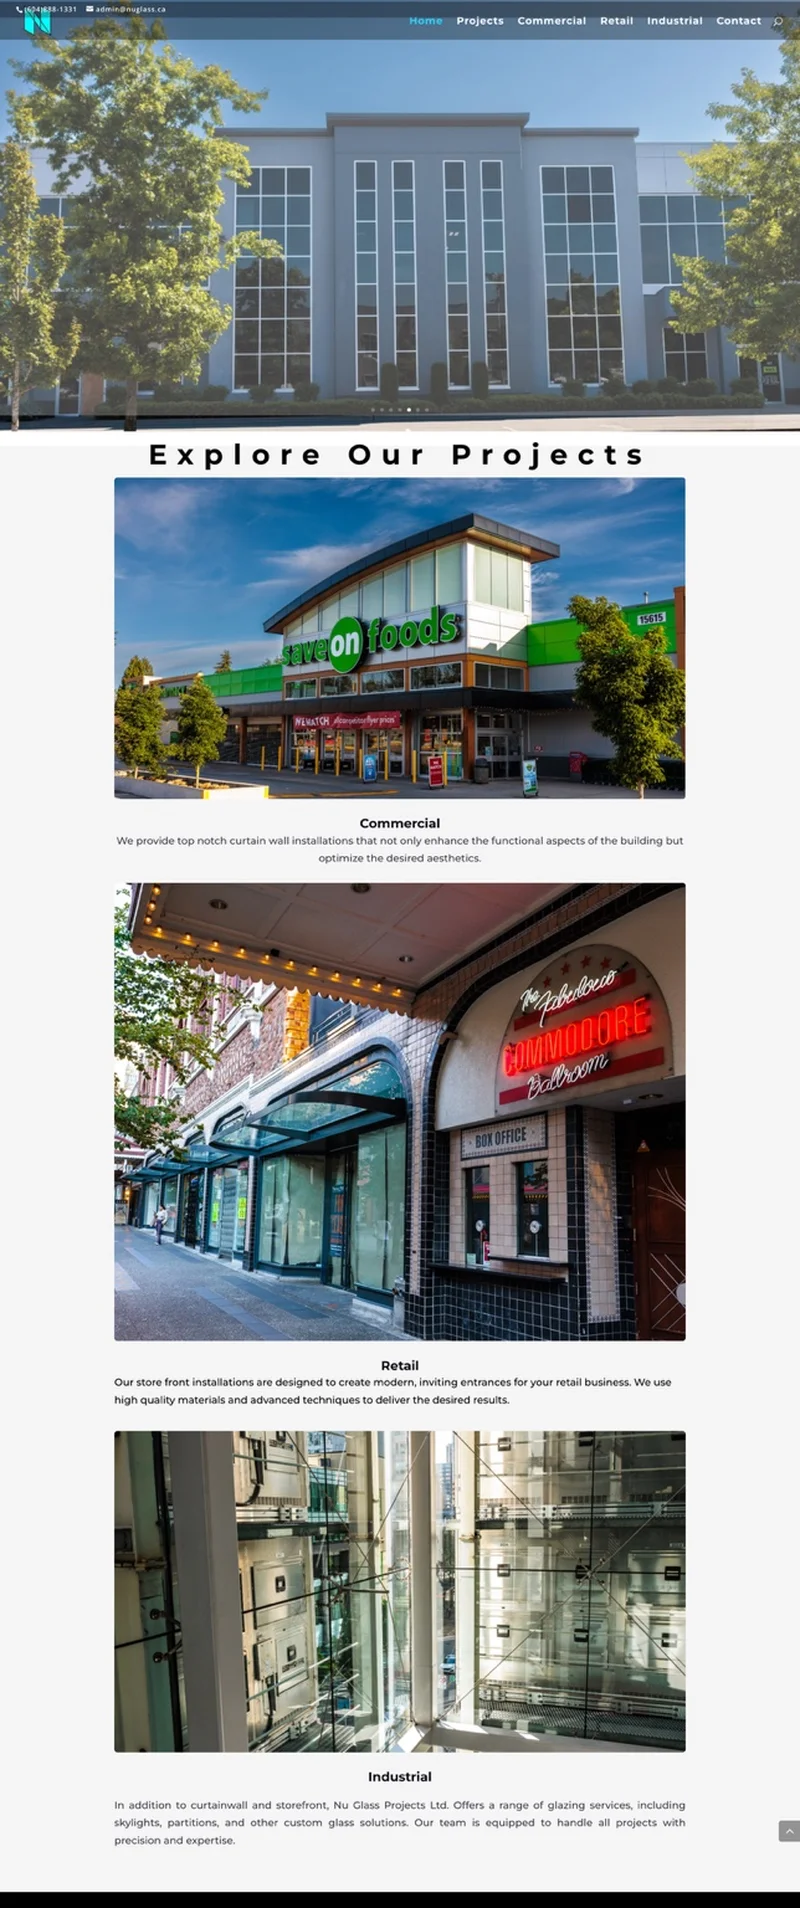
Glass manufacturing · BC
A hacked website recovered and stabilized with ongoing WordPress hosting and uptime support — in a case where no backup was available.
What you are left holding
Every cleanup ends with a written report, because “it’s fixed, trust me” is worthless the next time something looks odd. The report states when the compromise started as far as the logs show, the entry point we believe was used, the malicious files and database rows removed, the accounts and keys rotated, the components patched, and the hardening applied. Where a fact is uncertain, it says so instead of dressing a guess up as forensics.
It also lists what we filed on your behalf — the Google Search Console security review, any blacklist reconsideration requests — and what we could not do, which usually means the two or three things only you can decide: retiring an abandoned plugin, dropping an old admin account someone still uses, or budgeting for a rebuild the cleanup postponed rather than solved.
You can read an illustrative version before you hire us: see a sample after-action report. It is a redacted example written to show the format and depth — not a real client’s incident.
Who it is for
Our process
Confirm symptoms (redirects, spam, admin lockout), check hosting status, and decide whether to take a fresh backup before cleanup.
Point-in-time backup even if the site is compromised — useful for forensics and rollback if a cleanup pass misses something.
Malware scan plus core, plugin, and theme integrity checks against known-good copies.
Strip malicious code and users, update vulnerable components, and remove unused entry points.
WAF/CDN rules, least-privilege admin accounts, file permissions sanity check, and basic rate limits where they help.
Forms, checkout, logins, cron, and Search Console — then a reinfection prevention checklist you can actually follow.
Who does the work
Metro Vancouver IT is a small Burnaby-based shop. The person who triages the compromise removes the malware, rotates your keys, and writes your after-action report — so nothing gets lost in a handoff halfway through an incident.
Trusted technologies we support


Related services
Hardening and monitoring after an incident.
Learn moreWhich plugin we install, and what a week of attacks looks like.
Learn moreUpdates, backups, and monitoring.
Learn moreManaged hosting with WAF and backups.
Learn moreFAQ
Tell us what you are seeing — redirects, warnings, or admin lockout — and we will propose the fastest safe path. Typical cleanup totals $180–$270 (2–3 hours at $90 CAD/hour); heavier infections are quoted before we continue.
Contact
Include the website URL, warnings or redirects you see, and whether you still have hosting access. Active incidents are triaged the same business day when received during Pacific Time business hours.
Site hacked right now?
Contact
Tell us what you need help with and we will reply with clear next steps.


